From the tap of a payment card at a coffee shop to the swipe of an access badge entering a secure facility, RFID cards have become indispensable tools in access control, public transportation, retail, and logistics. This widespread adoption, however, has created a complex ecosystem fraught with challenges. Different vendors use proprietary protocols, security levels vary wildly, and the promise of seamless interoperability often falls short. In this environment, the role of RFID card certifications is paramount. These certifications are not merely bureaucratic hurdles; they are the essential, third-party validation mechanisms that ensure a card is both secure against sophisticated attacks and compatible with a global network of readers and systems. This article will explore how these certifications serve as the backbone of a secure, reliable, and interoperable RFID ecosystem, transforming a fragmented landscape into a unified, trustworthy technology.
1. What Are RFID Card Certifications?
RFID card certifications are third-party validations confirming that an RFID product meets specific security, communication, and interoperability standards. While many manufacturers claim compliance based on their internal testing, certifications represent objective, verifiable evidence issued by recognized standard bodies.
Certifications matter for four critical reasons:
- Standardization: They enforce a common language and protocol, ensuring that a card from one manufacturer can communicate effectively with a reader from another, preventing system fragmentation.
- Cybersecurity: They mandate the use of robust, tested cryptographic methods and secure memory structures, protecting sensitive data from skimming, cloning.
- Compatibility: They guarantee that the card’s radio frequency (RF) characteristics and data encoding adhere to global norms, enabling seamless use across different applications and geographies.
- Regulatory Compliance: They help organizations meet stringent legal requirements, such as data protection laws like GDPR and CCPA, by ensuring that the certified card reduces the risk of unauthorized data access.
2. Who Defines RFID Card Certifications?
The global landscape of RFID certification is governed by several key organizations, each focusing on a specific aspect of the technology, from the physical layer to the application layer.

2.1 ISO/IEC Standards
The International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC) define the foundational global standards for RFID communication and data structures. These standards govern the physical layer and the RF protocol, ensuring that the basic communication between a card and a reader is consistent worldwide.
- ISO/IEC 14443: This is the most widely adopted standard for contactless smart cards, used predominantly in payment and access control. It defines a short communication range (typically 7-15 cm) and a higher RF speed, making it ideal for “tap-and-go” applications where speed and security are paramount.
- ISO/IEC 15693: This standard is designed for medium-range applications, offering a read range of up to 0.9 meters. It is commonly used in logistics, library systems, and asset tracking where a slightly longer read distance is beneficial.
2.2 NFC Forum
The NFC Forum focuses on ensuring interoperability between NFC-enabled devices, which includes most modern smartphones, and NFC-compliant RFID tags and cards. The Forum defines the NFC tag types (Type 1 through 5) and the NFC Data Exchange Format (NDEF), which is the standardized data structure that allows applications to read and write information consistently, ensuring cross-device compatibility for mobile payments, pairing, and information exchange.
2.3 EMVCo
EMVCo is the body owned by major payment networks (Visa, Mastercard, etc.) that manages the EMV specifications for secure payment transactions. For contactless payment cards, EMVCo certification is mandatory. The process involves rigorous testing across three levels:
- Level 1 (L1): Focuses on the physical interface and the RF communication protocol, ensuring the card’s chip and reader can physically communicate according to ISO/IEC 14443.
- Level 2 (L2): Assesses the software application on the card, ensuring it conforms to the EMV Common Core specifications for transaction processing.
- Level 3 (L3): Tests the terminal’s conformity with the specific requirements of the payment network.
2.4 Common Criteria (CC)
For government-grade security and highly sensitive applications, the Common Criteria (CC) certification provides a deep security evaluation. CC is an international standard (ISO/IEC 15408) that assesses the security functionality and assurance of IT products, including smart card chips and operating systems. The assurance is measured by the Evaluation Assurance Level (EAL), ranging from EAL1 (functionally tested) to EAL7 (formally verified design and tested. High-security RFID chips, such as those used in e-passports or secure access systems, often achieve EAL4+ or EAL5+ ratings, signifying an extremely rigorous design, testing, and review process.
3. Certifications That Ensure Security
One of the primary reasons organizations rely on RFID card certifications is security. Cyberattacks and identity fraud are increasingly sophisticated, making certified cryptographic systems essential.

3.1 Cryptography Requirements
Certified cards move beyond simple identification to implement robust cryptographic security. This includes:
- Mutual Authentication: The card and the reader authenticate each other before exchanging any data. This mutual authentication prevents unauthorized readers from accessing the card’s data and stops cloned cards from tricking a legitimate reader.
- Encrypted Communication: Data transmitted between the card and the reader is encrypted, preventing eavesdropping (skimming) and ensuring that sensitive information, such as access keys or payment details, is never transmitted in plain text.
- Secure Key Storage: Certifications mandate that cryptographic keys are stored in protected memory areas within the chip, often secured by hardware-level anti-tampering mechanisms, making them resistant to physical and side-channel attacks.
3.2 Secure Data Structures
Certifications dictate how data is organized and protected on the chip. For instance, advanced cards like those based on MIFARE DESFire technology utilize sector-based access control. This means the card can host different applications (e.g., physical access, vending, library), and each application isolates and protects its own data with a separate set of keys. This way, a breach in one application does not compromise the others.
3.3 Compliance with Privacy Regulations
Data privacy laws like GDPR and CCPA require organizations to protect personal data stored in or transmitted by RFID cards. Certified cards provide a documented level of security assurance, reducing the risk of regulatory violations. Using uncertified systems could put the organization at risk of data breaches and legal consequences.
4. Certifications That Ensure Interoperability
While security is paramount, the utility of RFID technology is realized through seamless interoperability. Certifications ensure that systems are not fragmented by proprietary technology, fostering multi-vendor ecosystems.
4.1 Radio Frequency Standards
The ISO/IEC standards, particularly 14443 and 15693, define the precise RF characteristics—frequency, modulation, and coding—that a card must use. This is the fundamental layer of interoperability, guaranteeing that any reader designed to the 14443 standard can physically communicate with any card certified to the same standard. This avoids the costly and limiting scenario of proprietary reader-card pairings.
4.2 NFC Forum Type Definitions
The NFC Forum’s work on tag types and the NDEF format ensures application-level interoperability. For example, a card certified as an NFC Forum Type 4 Tag can be read by any NFC-enabled smartphone, regardless of the phone’s manufacturer or operating system. This consistency is vital for applications like digital business cards, smart posters, and mobile ticketing.
4.3 Protocol Consistency
Certifications enforce consistency in higher-level communication protocols. These protocols include anti-collision procedures, which allow multiple cards in the field to be read sequentially. They also include the Application Protocol Data Unit (APDU) command structure. With this consistency, developers can write software that reliably interacts with any certified card. This works regardless of the chip manufacturer behind the card. In addition, the standardization of Host Card Emulation (HCE) allows mobile devices to securely mimic a certified card. This standard further expands the ecosystem.
5. Why Non-Certified RFID Cards Are Risky
The appeal of non-certified, low-cost RFID cards is often outweighed by the substantial risks they introduce.

5.1 Security Gaps
Non-certified cards frequently cut corners on security. They may use older, compromised cryptographic algorithms, store keys in easily accessible memory, or even use hardcoded, default keys that are publicly known. This makes them highly vulnerable to:
- Cloning and Skimming: Simple, inexpensive devices can read and duplicate the card’s data, leading to unauthorized access or fraudulent transactions.
- Insecure Memory: Lack of secure data structures means that if one application is compromised, the entire card’s data can be exposed.
5.2 Fragmented Systems
Without adherence to global standards, non-certified cards lead to fragmented systems. A card may only work with a specific, proprietary reader, limiting the system’s flexibility and requiring costly replacements if the original vendor goes out of business or discontinues a product line. This vendor-specific lock-in stifles innovation and increases long-term operational costs.
6. Real-World Use Cases

The impact of certified RFID technology is evident across various sectors:
- Corporate Access Control: Companies rely on ISO/IEC 14443 certified cards with encrypted applications to manage physical access. The certification prevents attackers from easily cloning the access badge, which protects sensitive corporate assets and data.
- Public Transportation Systems: Many major cities adopt standardized, certified cards so passengers can use a single card across buses, subways, and regional rail lines, which promotes seamless travel and interoperability across different transport operators.
- Payment Cards: EMVCo certified contactless cards are the global standard for secure, fast transactions. Rigorous L1 and L2 testing verifies that the card’s chip and the terminal’s software can handle the transaction securely, no matter where the purchase happens.
- University or Hospital Ecosystems: A single, certified card can serve multiple functions—door access, cafeteria payments, library services, and parking—because the certification guarantees that the card’s chip can securely host multiple, isolated applications that comply with various reader systems across the campus.
7. How to Verify RFID Card Certifications
Before purchasing or deploying an RFID system, organizations should verify the certifications provided by the vendor. When evaluating a product, demand specific documentation:
- Certificate Number: A unique identifier issued by the certification body (e.g., EMVCo, Common Criteria).
- Test Report: The full report from the accredited testing laboratory detailing the tests performed and the results.
- Standard References: Explicit references to the specific ISO/IEC or other standards to which the card conforms.
8. Conclusion
In an increasingly connected world, secure identity and access control rely on trustworthy RFID systems. RFID card certifications provide the foundation for security, interoperability, and long-term scalability. They ensure that products meet international standards, protect against cyber threats, and work across different vendors and platforms. Looking for fully certified RFID card solutions that meet the highest standards of security and interoperability? Contact our team today to discuss your project requirements.
Recommended Product
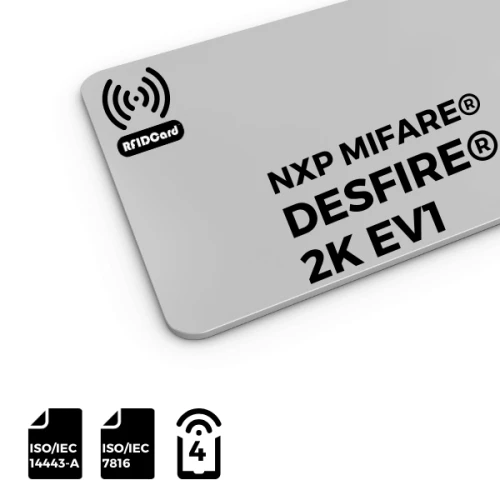
RFID Card CR80 MIFARE® DESFire® EV1 2K
The MIFARE® DESFire® EV1 2K RFID card is a secure, high-capacity contactless smart card ideal for various applications like access control, transportation, and payment systems. It features 2KB of integrated memory, advanced encryption standards for security, and is compatible with existing MIFARE® systems.
RFID Card NXP MIFARE® DESFire® EV3 4K
Blank or customized printing RFID cards with a choice of dimensions are available. The MIFARE® DESFire® EV3 4K is Common Criteria EAL5+ security certified for smart card IC products. The MIFARE® DESFire® EV3 4K ICs fully comply with NFC Forum Type 4 Tag.